Salesforce Authenticator

Screenshots
Details
- Rating
- 1.31K reviews
- Version
- 4.8.0
- Developer
- Salesforce.com, inc.
Analysis by Norviv
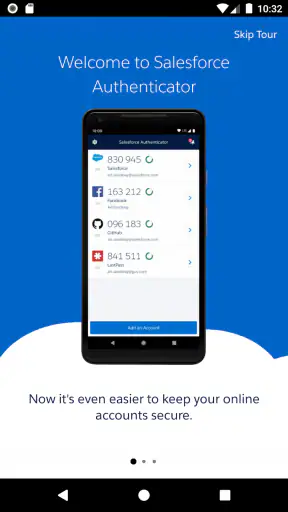
Two-step verification is one of those security habits that sounds simple until it interrupts a busy moment. Salesforce Authenticator is designed to make that extra check feel less like typing a temporary code and more like approving a request on a phone. I found that distinction important: the app is not a general password manager or a broad business dashboard. It is a focused security companion for confirming access to supported Salesforce accounts and services.
That focus makes it easier to understand what you are getting. Developed by Salesforce.com, inc., this free business app has been available since Nov 4, 2013, and its current version is 4.8.0. It is rated for Everyone, works from OS 9 onward, and has passed the five-million-install mark with a 4.4 average from roughly twenty-seven thousand ratings. Those figures suggest a mature, widely used tool, but they do not remove the need to think about how it fits your own login habits and network conditions.
How network access shapes the approval experience
I look at network access as part of the approval workflow, not just a technical detail: the browser, phone, and account all need to cooperate before a sign-in is complete. This section considers how to make that handoff less confusing when a workplace network, mobile connection, or managed device affects where an approval can happen.
The useful moment is the login request
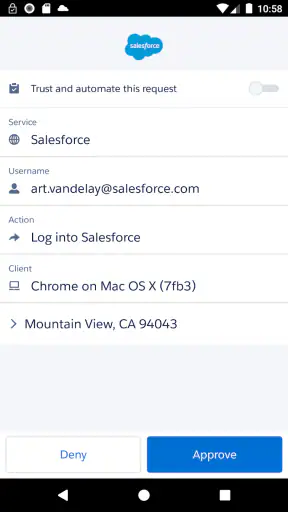
The central experience is straightforward. When a sign-in needs an additional verification step, the phone becomes the place where I review and approve the request. That is more comfortable than copying a one-time code from one screen to another, especially when I am signing in from a laptop and my phone is already beside me.
The convenience depends on the request reaching the phone and the approval being communicated back at the right moment. That makes connectivity part of the experience rather than a background detail. On a reliable home or office connection, the flow feels quick. In a crowded station, an elevator, or a building with weak reception, the same security step can become a pause while I wait for the notification or response to complete.
I would not treat this as a flaw unique to the app. Any verification method involving a live approval request can be affected by a poor connection. The practical lesson is to avoid beginning an important Salesforce login at the exact moment you are about to lose service. If I know I am moving between networks, I prefer to finish the sign-in before leaving a stable connection or keep another approved verification route available through the organization’s account setup.
Why approval prompts deserve attention
The best habit with an authenticator is also the simplest: approve only a request I recognize. A prompt arriving while I am actively signing in is different from an unexpected request appearing while the phone is in my pocket. The app’s value is not just speed; it gives me a deliberate checkpoint between a password and account access.
Stories Picked for You

Life360 Works Better When Your Household Agrees on What to Share

YouVersion Bible Fits Scripture into Everyday Phone Routines

Matchington Mansion Review: Match-Three Puzzles With a Place to Restore

Android Auto Shows Why Safer Driving Software Does Less

Google Find Hub Runs on Shared Devices and Quiet Trust

Sygic GPS Navigation: The Ultimate Offline Travel Companion
That checkpoint can be weakened by rushing. If several login attempts are made, or if a browser has been left open for a while, I take a second to identify what I am approving instead of tapping automatically. This is especially useful in a workplace where an account may be used across multiple browsers, devices, or locations.
There is also a small social advantage. A person who is not comfortable handling security codes can usually understand the idea of reviewing an approval request more quickly than the process of reading a code, switching apps, and entering it before it expires. That does not make the system foolproof, but it lowers the everyday friction that often causes people to weaken their security habits.
When the phone is not immediately available
The phone-centered design is convenient when I have the device with me. It is less convenient when the phone is charging in another room, has been left in a vehicle, or is unavailable during travel. This is one of the trade-offs I would explain before recommending it to a team: the second factor becomes tied to a physical object that people must remember, protect, and keep usable.
For a desk-based worker who keeps a phone nearby, that trade-off is minor. For someone who regularly works in areas with unreliable service or strict phone restrictions, it deserves more planning. The app can be a good part of a wider sign-in policy, but I would not assume that one phone-based method solves every recovery or access situation.
Using it across everyday mobile situations
On a normal workday, I can imagine the app being used in a simple sequence: I open a Salesforce session on a computer, enter my account details, check the phone when the approval arrives, and return to work. The phone does not need to become the main place where I manage business tasks. It serves as a confirmation device, which keeps the security action separate from the work itself.
That separation is useful when the main job happens on a larger screen. I do not have to hunt through a crowded mobile interface to find a security setting every time I sign in. At the same time, the app is still close enough to use when I am away from my desk and need to confirm access from a mobile browser or another supported sign-in context.
Travel changes the balance. A roaming connection, hotel Wi-Fi, captive portals, or a phone that is conserving power can all make a prompt feel less predictable. I would test the complete sign-in flow before an important trip rather than waiting until I am standing outside a client’s office. That test is not about measuring performance; it is about confirming that the account, phone, and approval process are all ready for the situation.
A realistic work scenario
Imagine I am leaving a meeting and need to review a Salesforce record from a borrowed laptop. I sign in, keep the phone unlocked and nearby, and wait for the verification request. If the connection is stable, approving it is less awkward than typing a code while people are waiting. I can then close the browser when finished instead of leaving an account open on a shared machine.
Now change one detail: the laptop is connected through a guest network that requires an extra sign-in page, while my phone is using a congested mobile connection. The approval may take longer, and I may not immediately know whether the delay comes from the browser, the network, or the authentication request. In that situation, I would avoid repeatedly tapping sign-in. I would check the connection, wait briefly, and then use the organization’s established recovery or alternative verification procedure if the request does not complete.
This is where the app feels most realistic to me. It removes code entry, but it does not remove the surrounding conditions of modern work: unstable networks, forgotten phones, locked-down devices, and shared computers. Good security tools reduce risk; they do not make every environment equally convenient.
What happens when approval fails
A failed approval can be frustrating because the user may not know which part of the chain broke. The request might not appear promptly, the phone might not have a usable connection, or the browser session might be waiting for a response that has already timed out. I would start with the least disruptive checks: confirm that the phone has connectivity, make sure I am looking at the correct account, and verify that the sign-in attempt is still active.
I would also avoid treating repeated prompts as harmless. If I did not initiate the login, I would not approve it simply because the request keeps appearing. If I did initiate it but the first attempt stalled, I would close the old attempt where possible before starting another. That reduces confusion and makes it easier to tell which request belongs to the current session.
For teams, the recovery plan matters as much as the initial setup. Before relying on the app for a critical account, I would ask the administrator what happens if the phone is lost, replaced, damaged, or unreachable. I would also learn whether the organization has another approved sign-in method. Those questions are not signs that the app is inadequate; they are basic preparation for any security factor attached to a personal device.
Replacing or losing a phone
A phone change is the situation I would take most seriously. An authenticator should never be treated like an ordinary app that can simply be reinstalled without considering account access. If the old device is still available, I would arrange the transition while I can sign in and follow the organization’s process. If it is lost, I would contact the relevant administrator or support channel promptly rather than experimenting with repeated login attempts.
This is also a reason to keep account recovery details current and to understand who controls access in a workplace. The app handles the approval part, but account ownership and recovery rules sit around it. A person using Salesforce through an employer may not have the same options as someone managing an individual business account, so I would confirm the procedure instead of relying on assumptions.
Does it use much data?
For ordinary use, the important network activity is the exchange of authentication requests and responses, not browsing through a content-heavy feed. That makes the app feel naturally suited to mobile connections. Still, I would not promise that it can function in every offline situation. The approval experience is connected to the sign-in process, so I would plan around the possibility that a missing or unstable connection can delay completion.
On a limited data plan, I would be more concerned with the surrounding login session than with the authenticator itself. Opening a full business website, loading records, or using a browser over mobile data can consume more attention and bandwidth than confirming a request. The sensible approach is to use trusted Wi-Fi when convenient, but not to join an unsafe network merely to make authentication easier.
Privacy-conscious users should also think about notification previews and lock-screen behavior. I prefer to keep sensitive details from being exposed in public notifications and to review the phone’s notification settings. That is a device-level choice rather than a claim about the app’s internal handling, but it affects how discreet the approval process feels in an office, airport, or shared household.
How it compares with codes and other authenticators
The usual alternative is a time-based code generated by an authenticator app. Codes can be useful when I need to read a number and enter it manually, and they may fit workflows where approval prompts are inconvenient. Their drawback is the extra switching and typing, particularly on a laptop with a long or complicated sign-in process. Salesforce Authenticator’s approval-oriented approach is more comfortable for people who value a quick confirmation over manual entry.
Another alternative is receiving a code by text message. Texts can be familiar, but they depend on cellular service and are generally less appealing to people who want to reduce reliance on phone-number-based verification. I would not choose a method solely because it is familiar; I would consider the organization’s security policy, the user’s travel pattern, and what recovery options exist.
Hardware security keys can be a better choice for users who want a physical sign-in device and work in environments where phone use is restricted. They can also be inconvenient to carry and manage. Salesforce Authenticator is the more natural fit when employees already keep their phones nearby and want an approval flow tied to that device.
Password managers may also offer authentication features, but they solve a broader problem: storing and generating credentials alongside other sensitive information. This app is narrower. I like that narrow purpose when I want a dedicated second step, but someone seeking one place for passwords, codes, secure notes, and identity management may prefer a fuller tool.
Small habits that make the experience safer
- Keep the phone close during important sign-ins, particularly when moving between Wi-Fi and mobile service.
- Read an unexpected approval request instead of dismissing it casually or accepting it automatically.
- Test the sign-in process before travel, a device replacement, or a major change in workplace network access.
- Learn the organization’s recovery procedure while the current phone still works.
- Protect notification previews if approval details could be visible to people nearby.
These habits are more valuable than trying to make the app do something it was not designed to do. The tool is strongest when the account owner understands the surrounding process and treats every approval as a meaningful security decision.
Who should use it, and who should look elsewhere?
I would recommend it to Salesforce users who want a less tedious second step than copying temporary codes. It suits employees who work from laptops, move between office and home, and usually keep a connected phone nearby. It is also a sensible option for people who find manual code entry confusing or easy to postpone.
I would be more cautious about recommending it as the only plan for field workers in areas with unreliable connectivity, people who cannot carry phones into their workspaces, or anyone who frequently loses access to their mobile device. Those users should first confirm that their organization supports a practical alternative and a clear recovery route.
The free price removes a direct purchase decision, and the Everyone age rating makes it broadly approachable. Even so, the real cost is operational: remembering the phone, responding to prompts carefully, and preparing for replacement or loss. That is a reasonable cost for stronger account protection, but it is still a cost in attention and planning.
My connectivity verdict
After looking at the app through the situations that usually cause authentication trouble, I see Salesforce Authenticator as a focused and approachable security tool rather than a complete identity-management system. Its approval flow can make Salesforce sign-ins feel natural, especially when I am working at a computer and the phone is within reach.
Its limits become clearer when connectivity is weak or the phone is unavailable. It does not make travel networks, shared devices, or account recovery disappear. I would choose it when the organization supports the workflow and the user can keep a dependable phone connection nearby. I would choose a different or additional method when offline-style access, phone-free authentication, or specialized hardware is more important.
With more than five million installs and a 4.4 average from about twenty-seven thousand ratings, it has the profile of an established business app rather than an experimental utility. For me, the strongest recommendation is simple: use it deliberately, prepare a recovery plan before you need one, and treat connectivity as part of the sign-in experience. That makes Salesforce Authenticator a practical choice for everyday two-step verification, provided its phone-based design matches the way you actually work.
Frequently Asked Questions
01What is Salesforce Authenticator and what is it used for?
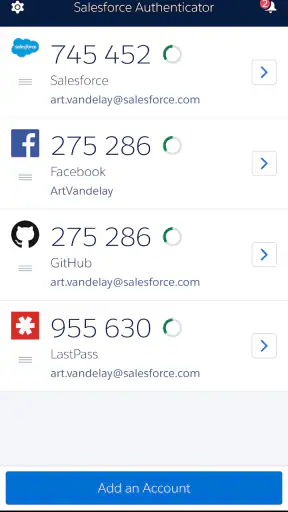
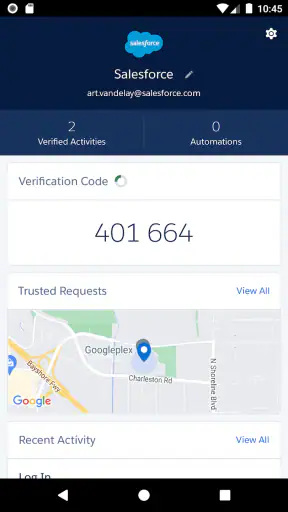
Salesforce Authenticator is a mobile security app that adds multi-factor authentication to supported Salesforce accounts and other compatible services. After linking the app to your account, it can send a login notification to your phone, where you approve or deny the request. Depending on the organization’s settings, it may also support location-based verification and time-based verification codes.
02How do I set up Salesforce Authenticator for the first time?
To get started, install Salesforce Authenticator from the official Google Play Store or Apple App Store, then open it and follow the pairing instructions. Your Salesforce administrator usually provides a two-word phrase or QR code to connect the app with your account. Once paired, approve a test login notification to confirm that notifications, account access, and device security are working correctly.
03Does Salesforce Authenticator work without an internet connection?
Salesforce Authenticator generally needs an internet connection to receive push notifications and communicate with the service during an approval request. However, supported configurations may allow you to use a temporary verification code generated inside the app when push approval is unavailable. Because offline behavior can depend on your organization’s Salesforce security settings, it is best to configure a backup verification method before traveling or losing network access.
04What happens if I lose my phone or get a new device?
If your phone is lost, stolen, damaged, or replaced, you should contact your Salesforce administrator or IT support as soon as possible so they can disconnect the old authenticator registration and help you enroll a new device. Do not assume that installing the app on a new phone automatically restores your account. Keeping recovery details and an approved backup authentication method can make the replacement process much easier.
05Is Salesforce Authenticator safe, and does it track my location?
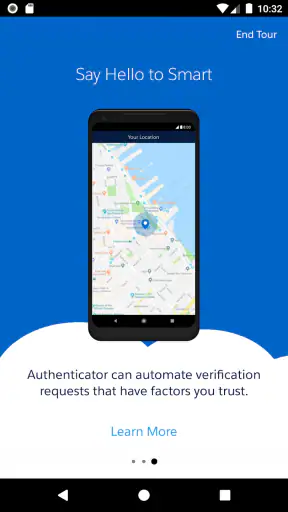
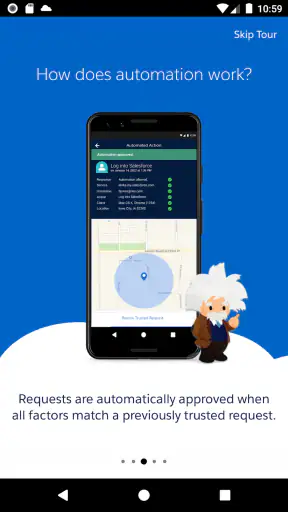
Salesforce Authenticator is designed to improve account security by requiring confirmation for sign-ins and displaying details such as the service, device, and approximate login location. If location-based features are enabled, the app may use your device’s location to recognize trusted places and automate certain approvals. You should review the permissions and privacy settings before enabling this option, and never approve a login you do not recognize.


